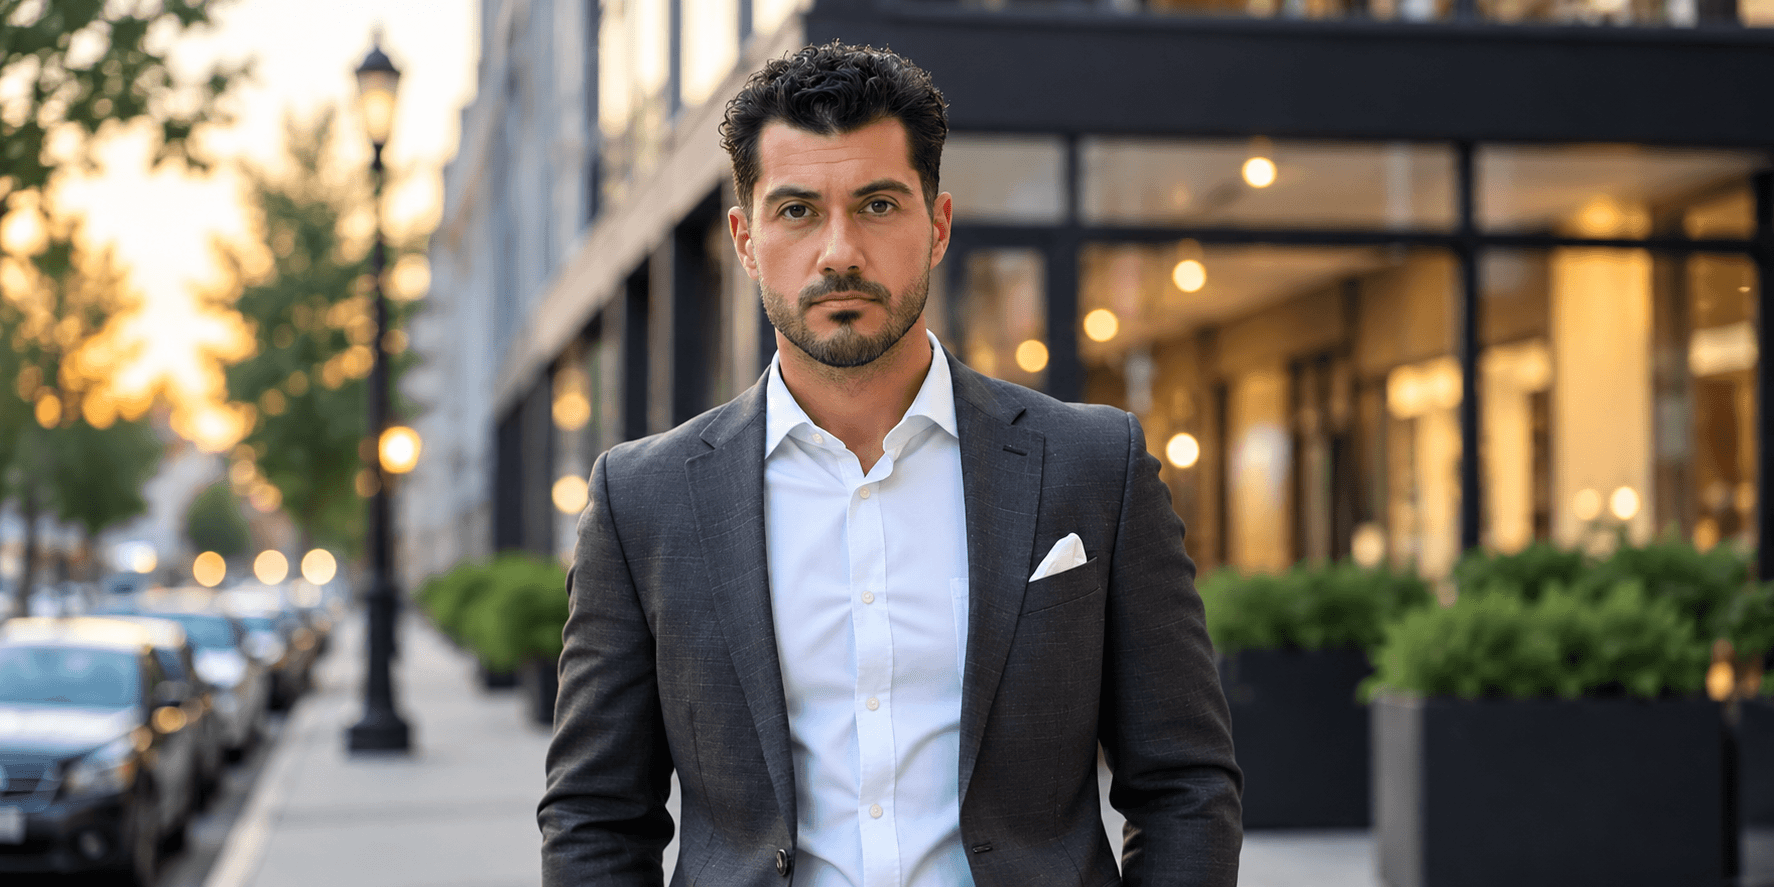
Employees are already putting client work into AI tools nobody approved. His SAFE framework gives leaders a practical way to find that use, decide what matters and put controls around it before a client, a regulator or an incident forces the issue.
Picture a common scene at an engineering firm. A project manager turns on an AI meeting assistant for a client call because it takes better notes than anyone on the team. The assistant records the call, transcribes the client’s design details and stores the summary in a service the firm has never reviewed. Nobody broke a rule on purpose. Nobody decided it was acceptable, either.
Michael J. Bannach, President and CEO of Stealth Technology Group (STG), says that is how most companies’ AI strategy actually gets made: one employee at a time. When he led a shadow AI assessment at a Fortune 500 company, the inventory surfaced 346 unsanctioned AI tools in use across 130 departments. “Nobody set out to break a policy,” Bannach said. “People found tools that made their jobs easier, and nobody asked where the data went. I see the same pattern in mid-sized firms, just with fewer zeros.”
The Exposure Is Measurable Now
The research has caught up with what Bannach sees in the field. In Microsoft and LinkedIn’s 2024 Work Trend Index, 78 percent of people using AI at work said they brought their own tools. In IBM’s 2025 Cost of a Data Breach Report, one in five of the breached organizations studied reported a breach involving shadow AI, and high levels of shadow AI added an average of $670,000 to the cost of a breach. Verizon’s 2026 Data Breach Investigations Report found that the share of employees using AI frequently on work devices had tripled in a year, to 45 percent.
Regulation is arriving in pieces. Texas’s AI law, in effect since January 1, 2026, gives companies that substantially follow a recognized AI risk framework, such as NIST’s, a defense for violations they catch through their own internal review. For a mid-market CEO, the details matter less than the direction: sooner or later a client questionnaire, an insurer or a board member will ask what AI the company uses and how it is controlled.
“The question isn’t whether your people use AI,” Bannach said. “It’s whether you can show a client, an insurer or a regulator that you know which tools they use and what data goes into them.”
The SAFE Framework
Bannach, a CISSP who holds a certificate in AI products and services from MIT, teaches a four-step approach he calls SAFE: Surface, Aim, Fence and Expand. He has presented it to CEO peer groups, and it is built for companies that will never hire a chief AI officer. The meeting assistant shows how it works.
Surface comes first: find what is actually in use before writing a single policy. Single sign-on logs, third-party app permissions, browser extensions, expense reports and a direct question to each department head will usually turn up the meeting assistant, along with a dozen tools nobody mentioned. “You can’t govern what you haven’t found,” Bannach said.
Aim is the business decision. Good meeting notes are worth having, so leadership approves the use case, names an owner and decides what success looks like, so AI spending and AI risk attach to something the company actually wants.
Fence puts controls around the approved tool: a business account instead of personal sign-ups, retention settings, contract terms on whether the vendor can train on company data, client consent before recording, and logging. The NIST AI Risk Management Framework and ISO/IEC 42001 give those controls a structure an auditor recognizes. The controls matter more than the paperwork; IBM’s 2025 report found that 97 percent of organizations that reported a breach of an AI model or application lacked proper AI access controls.
Expand is where the payoff lives. With the fence in place, the firm rolls the approved assistant out to every project team with training, measures whether it saves time, and retires the unapproved tools it replaces.
The order matters, Bannach said. Companies that start by banning tools drive usage underground. Companies that start by buying a platform often automate the chaos they already have.
What Good Looks Like
For a leadership team, success is not a policy binder. It is the ability to answer three questions on demand: what AI is in use, what data it touches and who is accountable for it. STG builds that answer into its AI strategy and governance work for regulated mid-market companies and defense suppliers, so it stays current as the tools change.
“Boards are starting to ask about AI the way they started asking about ransomware,” Bannach said. “The executives who come out of those conversations well are the ones who can show their work.”
Michael J. Bannach is President and CEO of Stealth Technology Group (STG), one accountable partner for IT, cybersecurity, compliance and AI for regulated mid-market companies and defense suppliers. STG is a Cyber AB Registered Practitioner Organization with teams serving Tampa, Sarasota, Boston and Greater Philadelphia. A CISSP with more than 25 years in enterprise IT and cybersecurity, Bannach also holds CCNP Enterprise and CCNP Collaboration certifications, a certificate in AI products and services from MIT, and an Executive MBA from Saint Joseph’s University. Learn more at michaelbannach.com and stealthtech365.com.
The Leader Report Contributor
Taylor McKenzie
Covers entrepreneurship, careers, technology, and the changing ways people build businesses and professional identities.
This article features partner, contributor, or branded content from a third party. Members of the The Leader Report editorial staff were not involved in the creation of this content. All views and opinions are those of the contributor alone.
HomePro Mobility: Keeping People Safely at Home
You may also like
Atlantic Health Strategies: Connecting Quality Care, Payer Readiness, and Operational Success
HomePro Mobility: Keeping People Safely at Home

How Jichél Stewart Helps Professionals Build Authority Beyond Their Job Titles
Rodrigo Coll Palma: Redefining Aesthetic Medicine
The Revenue Brian Muldoon Says Is Already Yours